AI-SecOps (SUVI-SG)
AI SOC Automation & Pentesting
Security alerts pile up by the thousand every day, and there are never enough people to check them. AI-SecOps (product name SUVI-SG, SmartDefense AI-SecOps) is a security operations platform where AI agents filter alerts, investigate the unclear ones and block what needs blocking. It also looks at your systems the way an attacker would, finding vulnerabilities first and telling you how to fix them. It installs in your own environment, whether an in-house server or the cloud servers you already use, and security logs are never sent to an outside AI service.
Last updated:
Too many alerts, too few people to read them
Out of thousands of alerts a day, only a handful are real attacks, and finding them takes up the analyst's whole day. Ransomware and account takeover attacks pick nights and weekends, and by morning it is often too late. Security staff are hard to hire, and even teams that want AI to help cannot send security logs and personal data to an outside AI service.
AI carries the work from detection through response
AI-SecOps works in the same order an experienced analyst does. Most events are settled automatically. Alerts that need judgment are investigated by the AI, which writes up its conclusion with evidence. Attack types are organized against MITRE ATT&CK, the international standard classification, and responses are proposed on the basis of your security policy. What must be stopped is blocked immediately or after an operator approves, depending on the risk. In our own test environment, running real attack scenarios, detection typically took 1 second from the start of an attack and blocking typically followed within 2 minutes (measured October 2026; results vary by environment).
What is SUVsoft's AI-SecOps?
SUVsoft has built mobile and email security products since 2011. We combined that with our experience running AI inside closed corporate networks to build AI-SecOps. It covers defense and attack testing in one product. It installs wherever you run, on in-house servers or cloud servers, and works in air-gapped networks. Some functions are also available through an API. People make the final call on important actions, and every action is recorded.
Key Features
AI threat detection
The flood of events is filtered automatically so people see only what matters. By learning normal behavior, it also catches slow attacks and intrusions that use stolen accounts.
Autonomous AI investigation
For alerts that need judgment, an AI agent looks up related records and presents recommended actions with its reasoning, grounded in your internal security policies and guidelines.
Automated response
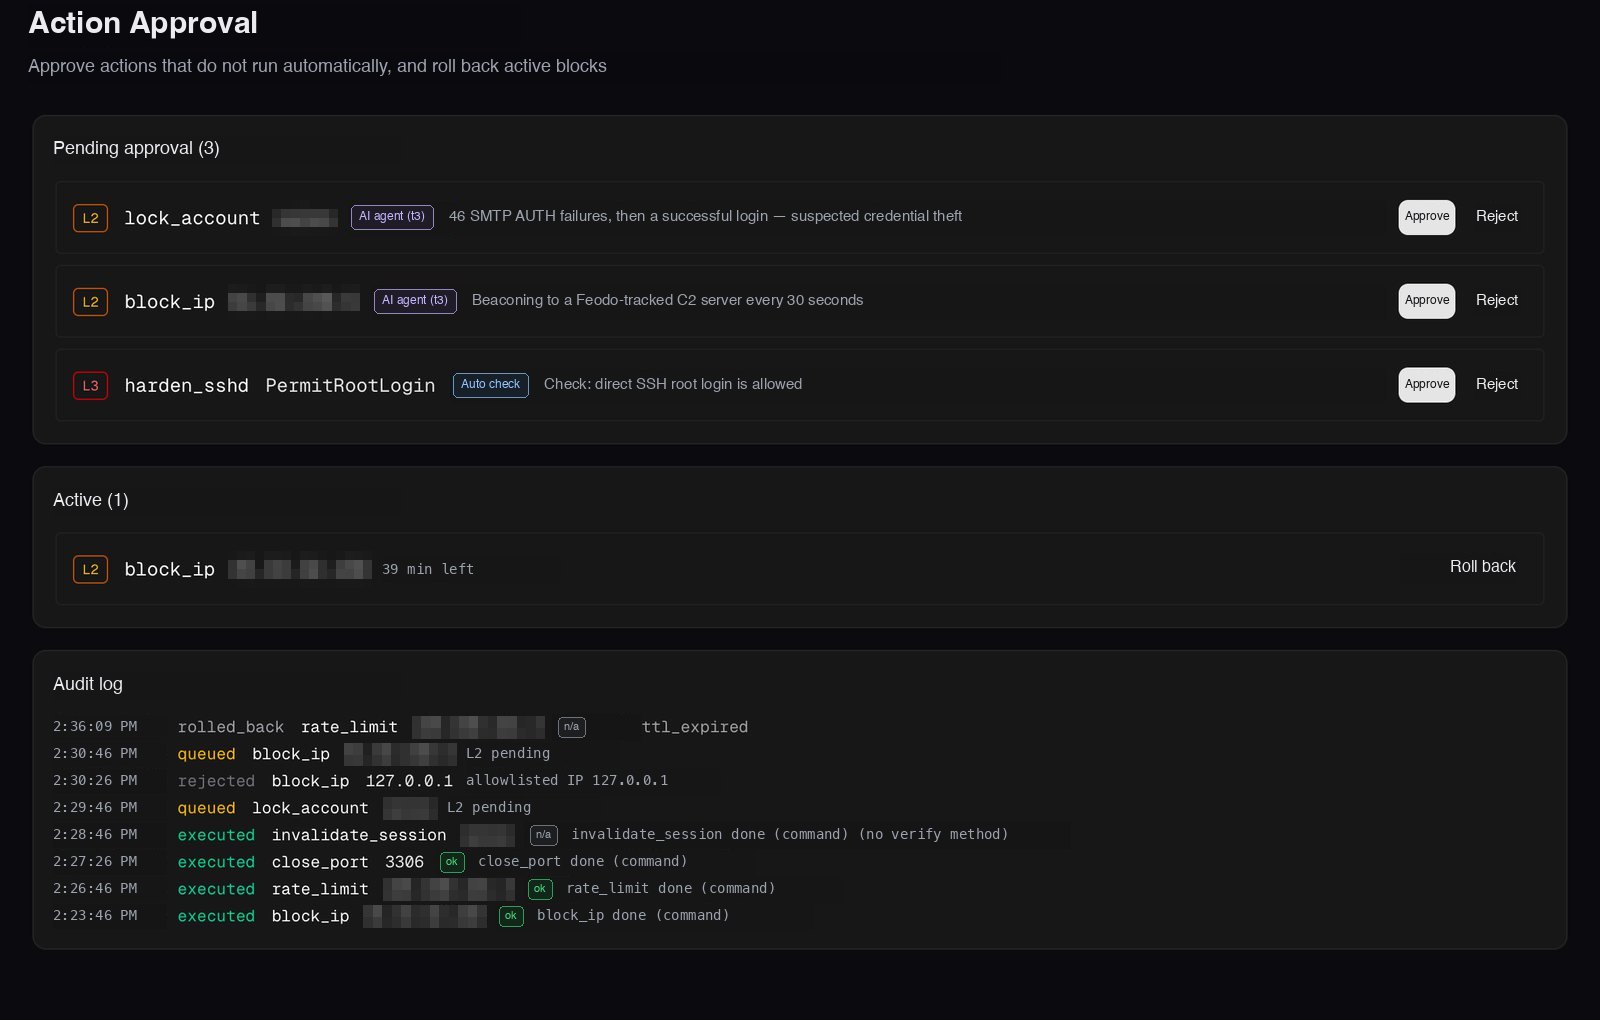
Threats are blocked immediately or after approval, depending on risk. Your organization sets how far automation may go, and any action can be rolled back.
AI attack testing
Enter a website address or connect a server and the AI tests it the way an attacker would, finds vulnerabilities and recommends a fix for each one.
Defense status at a glance
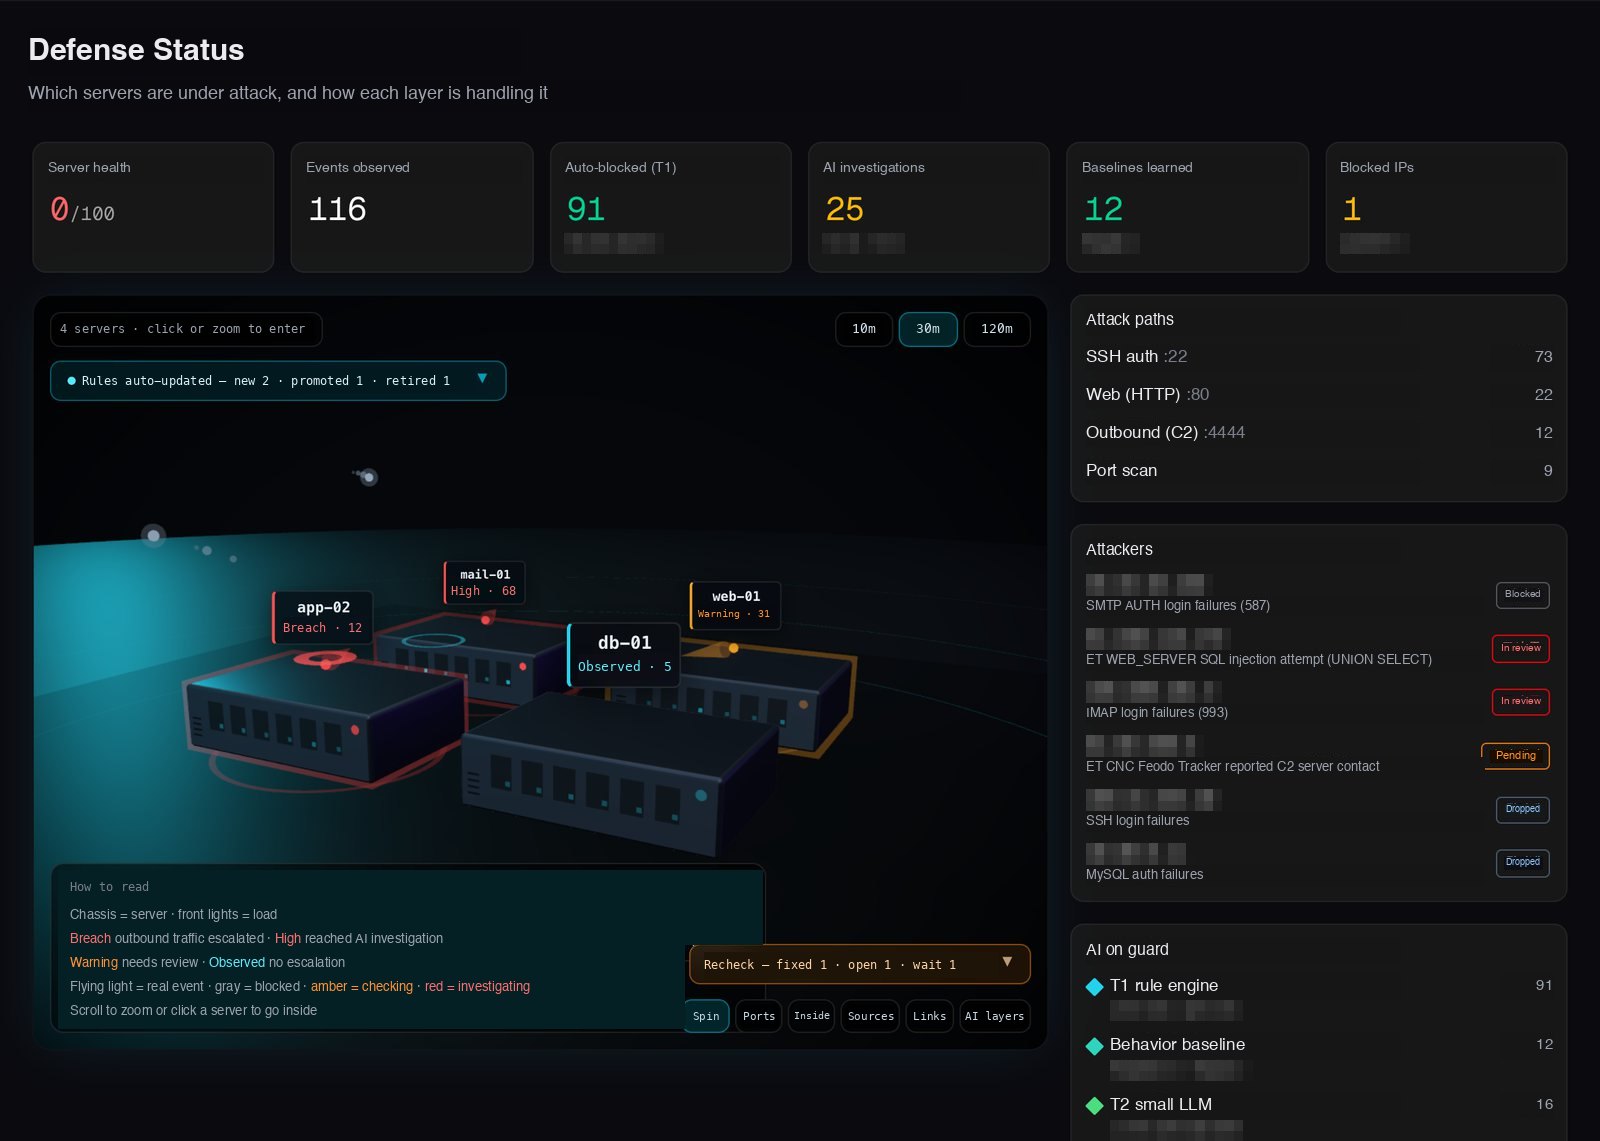
Scattered alerts are grouped into incidents. A 3D view shows which servers are under attack and how far the attack has been stopped.
Reports and audit trail
Findings, risk levels and responses are compiled into reports suited to each role. Views, searches and configuration changes are logged for later audits.
Deployment that fits your environment
It runs on in-house servers (on-premises) and also works as soon as it is installed on the cloud servers you rent. Some functions can be integrated through an API, and the analysis AI runs inside your environment so security logs are not sent to an outside AI service.
Specifications
Detection & Analysis
- Threat detection
- Rule-based detection, behavior learning and AI analysis working together
- AI investigation
- AI agents gather evidence and write the report
- Incidents
- Related alerts grouped into a single incident
- Threat classification
- Attack types classified against MITRE ATT&CK
Response & Testing
- Automated response
- Runs automatically or after approval by risk level, with rollback
- Attack testing
- AI finds vulnerabilities in websites and servers and recommends fixes
- Server checks
- Finds weak security settings and re-checks after the fix
Deployment & Operations
- Deployment
- On-premises, cloud server install, or API integration. Supports air-gapped networks
- AI runtime
- Runs inside your environment. Nothing sent to external AI services
- Reports & records
- Role-based reports, audit record of every action, chat and email notifications
How Deployment Works
- 1
Environment review
We go over the servers to watch, the security tools you already use and your network layout.
- 2
Installation
Installed where you run, on an in-house server or a cloud server. It starts in a watch-only mode that does not block anything.
- 3
Detection tuning
The system learns normal behavior and we review the detection results together.
- 4
Response scope
You decide which actions run automatically and which need approval.
- 5
Operation
Automated response is switched on and only the items that need review arrive as notifications.
In Practice
“One or two security staff, often part-time”
Instead of opening alerts one by one, staff review organized incidents and focus on the decisions that need approval.
“AI-assisted monitoring inside a separated network”
The analysis AI is installed inside the internal network, so security logs never leave, and every action is recorded.
“Covering the hours when nobody is there”
Threats are blocked first within the scope you set. In the morning, a report shows what was blocked and why.
“Running services on cloud servers”
Install it on the cloud servers you use for web or database workloads and it starts watching right away. You get security operations without adding separate equipment.
“Checking for vulnerabilities before going public”
Enter the website address and the AI runs the attack test. Run it whenever you need and get the fixes along with the findings.
FAQ
A SIEM collects logs and raises alerts. A SOAR runs playbooks that people wrote in advance. AI-SecOps does the work in between: the AI checks whether an alert is real and decides what it means. People review the results and make only the important decisions.
No. The analysis AI is installed in your environment, on an in-house server or your own cloud server, and runs only there. It can also be installed in air-gapped networks with no internet connection.
On-premises on your in-house servers, installation on the cloud servers you rent, or API integration for just the functions you need. If you run your web or database servers in the cloud, install it there and it works right away. Contact us and we will suggest a setup that fits your environment.
Yes. Detected attacks are organized by MITRE ATT&CK tactics and techniques, together with a response that follows your security policy.
High-impact actions run only after an operator approves. Blocks that were applied automatically expire after a set time and can be rolled back at any moment. Your organization decides how far automated response may go, and every action is recorded.
AI-SecOps watches the behavior that shows up during an intrusion, not one specific piece of malware. It catches early signs that lead to ransomware or data theft, such as a successful login after repeated failures, unusual access, or suspicious outbound traffic, and blocks them early.
Yes. Enter the website address to test or connect a server, and the AI tests it the way an attacker would, finds vulnerabilities and writes up how to fix them. Tests are run only against your own systems, with authorization.
They were measured in our own test environment in October 2026 using real attack scenarios. Results depend on your environment and policy.
Mid-sized and smaller companies with few or part-time security staff, public-sector and financial organizations that must keep networks separated, organizations that cannot staff monitoring at night and on weekends, and teams that run their services on cloud servers. Contact us and we will walk you through a setup that fits your environment.
Interested in AI-SecOps (SUVI-SG)?
Leave your info and our team will reach out shortly.
Related News
All news